How to Conduct an Effective Table-Top Exercise
An exercise that is limited to reviewing a business continuity plan does not measure an organization’s actual ability to make decisions under pressure. Knowing how to conduct a tabletop exercise involves precisely bringing the right people together to address a credible scenario, identifying dependencies, and transforming identified gaps into verifiable improvement actions. The goal is not to demonstrate that the BCP exists, but to verify that it can be activated, understood, and managed within timeframes compatible with critical operations.
A tabletop exercise is particularly well-suited for organizations that wish to test their crisis governance, escalation procedures, communication mechanisms, and the coordination between business continuity, IT, cybersecurity, and business functions. It does not replace a technical recovery exercise or a full-scale simulation. However, it helps prepare for these more demanding tests by first clarifying decisions, responsibilities, and interfaces.
Define what the exercise is actually supposed to test
The quality of a tabletop exercise is determined before it even begins. Before drafting the scenario, it is essential to define a specific, observable test objective that is linked to a precise resilience challenge. Attempting to test the activation of the crisis response team, IT recovery, customer communications, fallback solutions, and regulatory compliance all at once often results in an exercise that is too broad in scope and yields only superficial insights.
For example, an objective might focus on the ability to classify a cyber incident affecting a critical application, decide whether to activate the business continuity plan, prioritize which operations to maintain, or coordinate communication with authorities and stakeholders. Each objective must be linked to specific evaluation criteria. This makes it possible to distinguish between issues stemming from a documentation gap, a governance flaw, a lack of resources, or insufficient mastery of a skill.
The scope must be clearly defined. It includes the relevant processes, sites, service providers, information systems, participants, and the hypothetical time period covered by the exercise. This clarity prevents a common problem: participants respond by referring to capabilities that are not available in the scenario or that have never been validated.
Choose a plausible scenario, without making it too comfortable
A good scenario is credible in light of the risk analysis andthe business impact analysis. This could include prolonged unavailability of a critical supplier, a ransomware attack, loss of access to a site, a telecommunications outage, or the unavailability of key personnel. Its value lies less in its dramatic nature than in its ability to prompt difficult decisions.
The scenario should reveal information gradually. An initial prompt may signal an anomaly or an outage. Subsequent scenarios clarify the scope of the incident, introduce an additional constraint, or present participants with a request from a customer, a regulator, or the media. This progression replicates the uncertainty of a crisis situation without attempting to trap the teams.
It is helpful to establish clearly stated working assumptions: whether or not collaborative tools are available, the status of backups, the availability of service providers, the capacity for remote work, or the expected duration of the disruption. A scenario that is too vague encourages theoretical responses. Conversely, an overly detailed scenario traps participants in a prewritten response. The appropriate level of detail depends on the organization’s maturity and the chosen objective.
How to Conduct a Table-Top Exercise During a Session
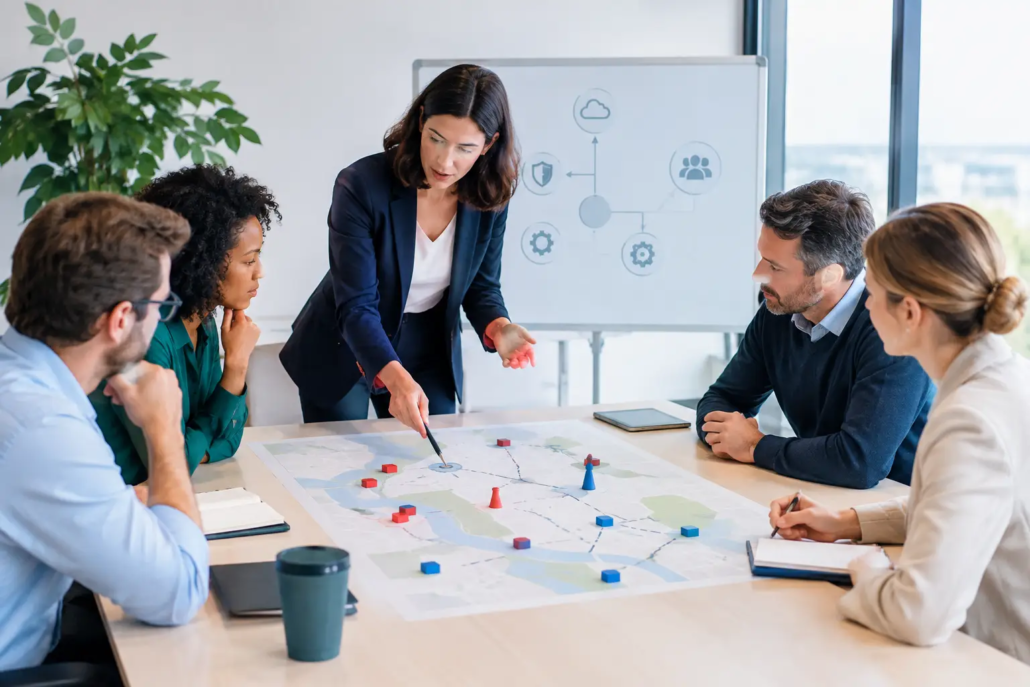
The session is based on a clear division of roles. The exercise facilitator sets the framework, presents the rules, and ensures that the time limit is respected. The moderator presents the prompts, asks questions, and keeps the discussion moving without providing answers on behalf of the participants. Observers record decisions, deadlines, deviations, and points requiring further discussion. Finally, participants play their own organizational roles and rely on the resources actually available to them.
From the outset, it is important to note that this exercise is neither an individual audit nor a hierarchical evaluation. This rule promotes transparency, particularly when procedures are vague or responsibilities overlap. Participants must be able to point out when information is missing, when a decision has not been assigned, or when a contingency plan has not been tested.
The workshop should focus on decision-making questions. Who classifies the incident? When is the crisis response team convened? Which authority approves a service interruption? How are priority activities determined if multiple business units are vying for the same resource? What contractual or regulatory obligations require notification? These questions compel teams to align the documentation system with operational realities.
The facilitator must also prevent two common pitfalls. The first is turning the exercise into a problem-solving meeting, where participants immediately devise a future solution. The second is accepting general responses such as “we’ll contact the service provider” without identifying who is responsible, the channel of communication, the timeline, and the alternative plan in case of failure. When a deviation occurs, it must be noted and then addressed in the debriefing.
A two- to three-hour session is often sufficient to test a well-defined crisis scenario. Beyond that, attention wanes and the decisions made become less useful. For a complex scenario, it is better to organize several targeted exercises than a single, overly ambitious event.
Look at the facts, not just the quality of the discussions
The evaluation must focus on verifiable elements. Observers are not seeking to judge the participants’ ease or comfort, but rather the group’s collective ability to apply the intended mechanisms. In particular, they may note:
- the time required to detect, assess, and escalate the incident;
- clarity regarding roles, delegations of authority, and decision-making thresholds;
- effective access to critical contacts, procedures, tools, and information;
- alignment between business priorities, recovery objectives, and technical capabilities;
- the quality of internal, external, contractual, and regulatory communications.
These observations should be considered in light of the governance requirements defined in the business continuity management system. Within a framework based on ISO 22301, this exercise helps demonstrate that continuity strategies and procedures are tested and improved in a planned manner. The goal is not to produce formal evidence disconnected from real-world conditions, but rather to have concrete information to guide continuous improvement.
Turning Feedback into an Improvement Plan
The value of a tabletop exercise becomes clear after the session. A report must be prepared promptly, while the facts and decisions are still fresh in everyone’s minds. It identifies effective practices, observed discrepancies, invalidated assumptions, and decisions that require further validation.
Each action must be formulated in operational terms: a designated person in charge, a deadline, a priority, and a completion criterion. “Update the BCP” is too vague. It is preferable to specify, for example, that the business continuity manager will update the activation procedure to include delegations of authority outside of business hours, and then have it validated and tested during an upcoming exercise. This level of detail facilitates monitoring by the business continuity governance team.
Not all deviations are equally critical. The absence of a secondary point of contact can be corrected quickly. An unmanaged dependency on a service provider, ambiguity regarding the authority to shut down a service, or an inability to communicate outside the corporate network require a more in-depth analysis. Prioritization must take into account the impact on critical operations, regulatory requirements, feasibility, and the level of residual risk accepted by the organization.
A new exercise must then verify the effectiveness of the corrections made. It is this cycle—prepare, practice, analyze, correct, and repeat—that drives progress in operational resilience. The most mature organizations do not seek to produce a perfect exercise. They build a sustainable capacity to recognize their vulnerabilities, make decisions methodically, and improve their systems before a major incident puts them to the test.
This post is also available in:


